MIST Integration + Huntress
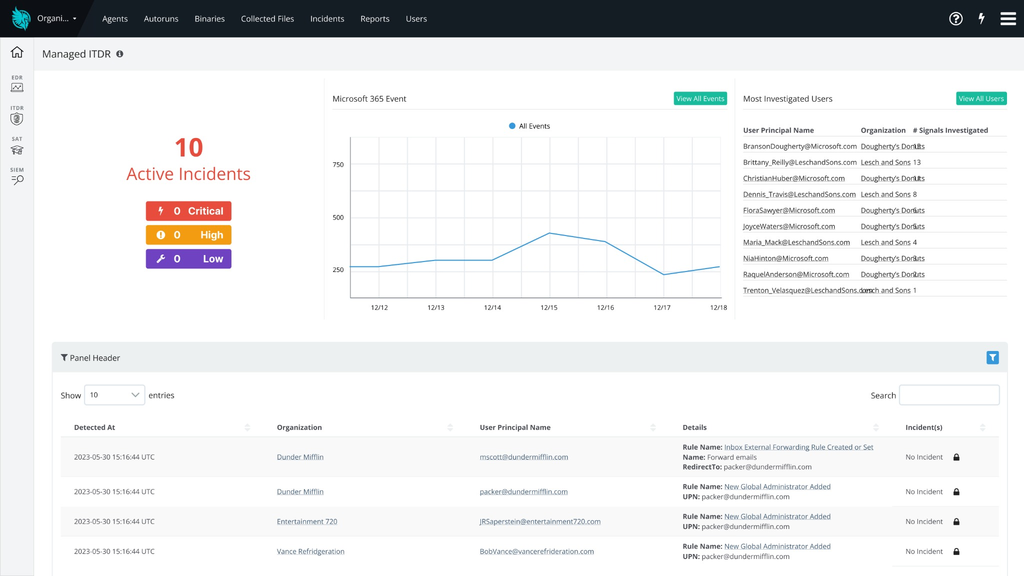
Managed ITDR
24/7 identity threat detection and response for your connected cloud environment.
Protect the accounts attackers want to use
Stolen passwords and session tokens can let attackers act as legitimate users. Identity Threat Detection and Response looks for suspicious behaviour that can signal account compromise, including attacks that evade an initial authentication check.
MIST partners with Huntress to monitor supported Microsoft 365 and Google Workspace environments, with Huntress analysts investigating suspicious identity activity around the clock.
Detect and respond to identity threats
Suspicious account activity
Investigate unusual sign-ins, changes in behaviour and activity that could indicate credential theft or account takeover.
Session hijacking
Look for signs that an attacker is abusing session tokens or using adversary-in-the-middle techniques.
Mailbox and application abuse
Investigate malicious inbox or forwarding rules and potentially rogue OAuth applications, where supported by the connected platform.
Investigation and remediation
Huntress validates findings and uses supported response actions to help contain identity threats. MIST coordinates customer communication and follow-up.
Reduce business email compromise risk
Attackers can quietly change mailbox rules, intercept conversations and impersonate trusted contacts. Identity monitoring helps identify this activity so the affected accounts and business processes can be reviewed.
Fit the service to your organisation
We confirm the tenants, identities, permissions, integrations and escalation contacts in scope. Supported detections and response actions vary by platform. MFA, access controls and staff awareness remain important parts of your wider security programme.
Let’s strengthen your security
Talk to MIST about your environment, existing controls and the level of managed protection you need.
sales@mist-integration.com.au · Williamstown, Victoria, Australia