MIST Integration + Huntress
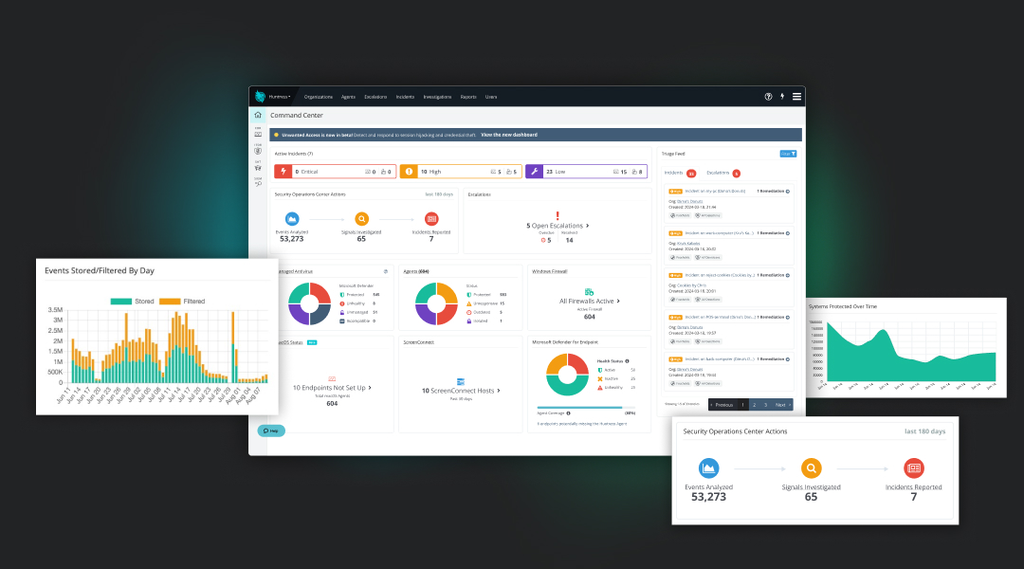
Fully Managed SIEM, SOC, ISPM & ITDR
24/7 security expertise. Managed by MIST, powered by Huntress.
Protection beyond antivirus
Attackers use stolen credentials, legitimate administration tools and new techniques to avoid detection. Protecting your organisation means understanding weaknesses, recognising suspicious behaviour and having people ready to investigate and respond.
MIST Integration partners with Huntress to bring together purpose-built security technology and a 24/7 human-led, AI-assisted Security Operations Centre. You gain access to security specialists without having to build and staff an internal SOC.
We help you select and deploy the right services, coordinate with Huntress, explain findings and support the next steps for your business.
Four connected security services
Managed SIEM
Collect and analyse relevant security logs across supported systems. Gain investigation context, prioritised findings and searchable evidence.
24/7 Managed SOC
Huntress analysts monitor, investigate and validate suspicious activity, with response actions available through the connected services.
Managed ISPM
Strengthen Microsoft 365 identity settings through managed policies, posture assessment and configuration-drift remediation.
Managed ITDR
Detect and respond to suspicious identity activity, account takeover attempts, session hijacking and malicious mailbox changes.
One coordinated response
1. Understand and onboard
MIST reviews your environment, confirms coverage and connects the agreed endpoints, identity platforms and log sources.
2. Monitor and investigate
Huntress’s SOC reviews suspicious activity around the clock, using technology to accelerate investigation and human judgement to validate threats.
3. Contain and communicate
Supported response actions help contain confirmed threats. MIST coordinates customer communication and the business decisions that follow.
4. Recover and improve
We help prioritise recovery tasks and improvements to access, configuration, monitoring and staff awareness.
Support your Essential Eight uplift
Security improvement is an ongoing process. Managed logging, investigation and identity hardening can support that work alongside application control, patching, MFA and tested backups.
The right maturity target and evidence depend on your environment. We can help review gaps and plan improvements; these services support a broader control programme and do not automatically establish an Essential Eight maturity level.
A clear scope from the start
We confirm supported platforms, log sources, retention requirements, licences, response permissions and escalation contacts before deployment. Endpoint isolation and remediation depend on the endpoint detection and response services in your agreed scope.
Let’s strengthen your security
Talk to MIST about your environment, existing controls and the level of managed protection you need.
sales@mist-integration.com.au · Williamstown, Victoria, Australia